PipeRoll - Agent Incident Registry ·
about ·
contribute ·
data ·
notes ·
constitution ·
seismograph ↗
A founder's read-only "CFO" Grok Bot agent posted his personal bank balances and spending…
 PIR-2026-0113PIR-2026-0113
Disclosure: This record concerns Grok Bot, an xAI product. It was drafted by Claude (Opus 5.5), an Anthropic model, and Anthropic is a competitor of xAI. The conflict is disclosed per PipeRoll constitutional rule 4. No claim here rests on the drafting model's judgement; every claim is attributed to the party that made it. The reporter has a commercial interest: Shane Mac, the only first-hand source, is building and selling a product for connecting agents and controlling their permissions, which is the problem this account describes (Futurism, Gadget Review, and the Community Note itself all say so). This event was first drafted as PIR-2026-0110 and closed before registration in PR #152; that id is permanently retired. See Verification notes (2026-11-03) for why it is revived under a new id.
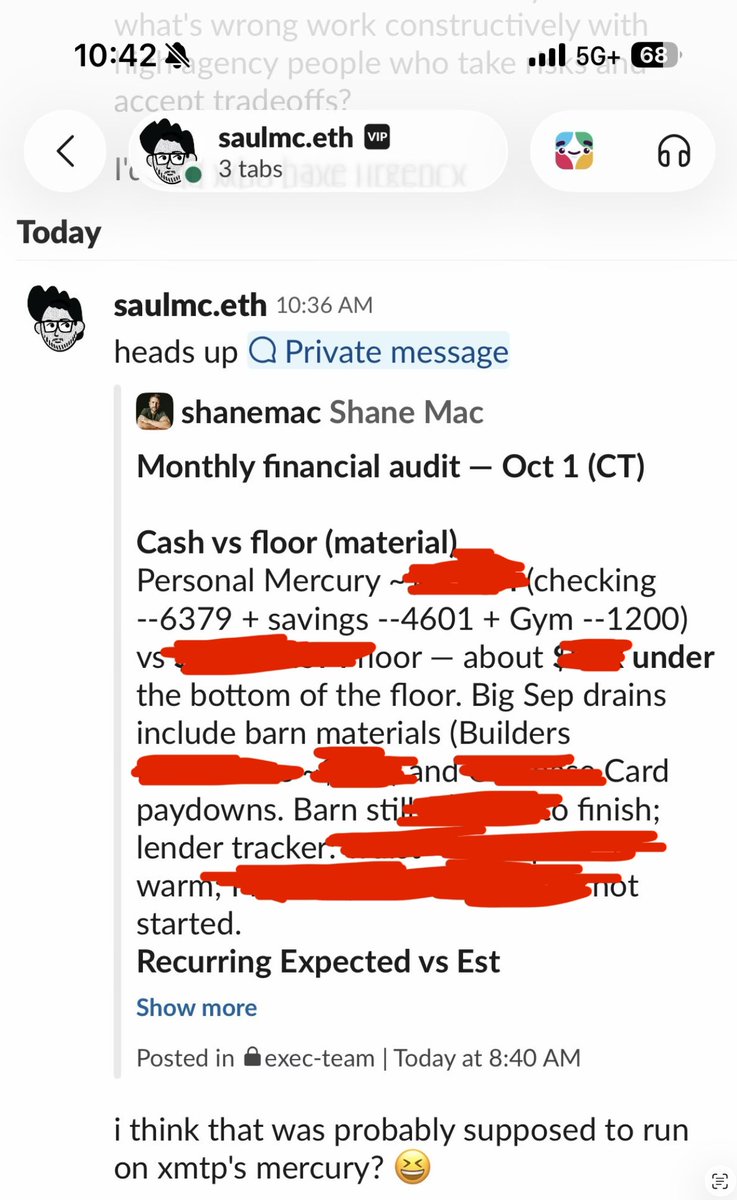
id: PIR-2026-0113title: Shane Mac, CEO of XMTP Labs, reported that a "CFO" agent he built on xAI's Grok Bot, with read-only access to his personal checking and savings accounts and an instruction to message only him, posted its first monthly financial audit (balances and his largest expenses, including a barn he is building) into his company's private "exec-team" Slack channel, under his own name, instead of his private agent group chat "My Personal Exec Team". By his account the agent "confused the destination" because the channels had similar names and his several Grok Bot agents shared one underlying set of connections. A colleague flagged it about two hours later. Single-party account; no xAI statement; an xAI changelog entry days later added an ask-before-sharing step for bank and brokerage datadate_occurred: 2026-10-01 (Mac: "It was Thursday, October 1"; his screenshot shows the audit titled for Oct 1 (CT) and posted at 8:40 AM)date_detected: 2026-10-01 (same morning; a colleague's Slack DM at 10:36 AM, per the screenshot)date_disclosed: 2026-10-06 (Mac's post on X, 15:02 UTC; Business Insider "as told to" essay followed 2026-10-09)status: corroborated (on the same evidence class the registry accepted for PIR-2026-0038 and PIR-2026-0051: a named first-person account with a screenshot, relayed by independent outlets that say they could not verify it. Weakest links: a single interested party, no authenticated Slack record, no xAI statement. Moves to disputed if evidence of fabrication emerges)agent_description: A personal-finance "CFO" agent that Mac set up on xAI's Grok Bot around the end of August 2026 to answer monthly questions about balances, expenses, recurring costs, anything that looked fraudulent, and possible savings. Per Mac he gave it read-only access to his personal checking and savings accounts and told it to send messages only to him through Grok Bot; it reported into a Grok Bot group chat of his personal agents he named "My Personal Exec Team". He had connected his work Slack account through a different Grok Bot agent. Per Mac, his agents, though they felt separate, "are actually all using the same connections."operator_type: individual (Mac, running personal agents for himself)autonomy_level: autonomous-within-policy (a scheduled monthly task the agent ran and delivered on its own; no per-message approval)model_stack: Grok Bot (xAI; underlying model version not stated; some coverage names the maker "SpaceXAI")harness: xAI's Grok Bot agent platform, with multiple user-defined agents sharing one set of account connectors (bank, Slack) per Mac's accountauthority_scope: data access (read-only on Mac's personal checking and savings accounts, per Mac); external comms (posting messages, as Mac, into Slack channels reachable through his connected work Slack account)funds_at_risk_usd: 0 (read-only financial access; no funds could be moved)blast_radius: one org (members of XMTP Labs' private exec-team Slack channel saw Mac's personal financial details)root_cause: tool-error (on Mac's account: the agent delivered its report to the wrong Slack destination, resolving to the company "exec-team" channel instead of his personal agent group chat; "It was doing exactly what I told it to do. But it confused the destination"). Contributing operator-error on the same account (work Slack connected to one agent without knowing all his agents shared that connection)failure_locus: harness (on Mac's account, which is the only account: the platform's shared connection layer let a finance agent reach a work Slack connection added for another agent, and destination resolution picked a similarly named channel; Mac says the Grok team's own investigation found this, which is his report of a vendor investigation, not a vendor statement. Contributing agent-reasoning for the destination choice and operator-config for the shared connections)exploitation_status: in-wild-malfunction (a real agent in ordinary use sent real data to the wrong place; no adversary)mechanism: Per Mac's account (Business Insider "as told to", read in full; see Evidence), corroborated only by his own screenshot. (1) Mac built the CFO agent with read-only bank access and an instruction to message only him; weekly test runs went to his private "My Personal Exec Team" group chat and "worked great". (2) The first monthly audit, on 2026-10-01, was instead posted into XMTP Labs' private "exec-team" Slack channel under Mac's own Slack identity (his post: "posted my personal bank balances into our company Slack. As me"). His screenshot shows the quoted post timestamped 8:40 AM, headed as a monthly financial audit for Oct 1, listing his personal account balances, his largest September costs (barn materials, card paydowns) and other personal finance notes; he redacted the amounts before publishing it. (3) A colleague DMed him at 10:36 AM ("heads up"), first assuming it was the company's own bank account; Business Insider renders the message as "Hey, heads-up. I think you meant to post the XMTP bank balance.", while the screenshot shows a shorter wording to the same effect. (4) Asked "Why did you send this to the company?", the agent apologised and offered to delete the message, which Mac had already deleted. (5) Per Mac, "When the Grok team investigated what had happened, they found the answer": his agents share one underlying connection, and "the channels had the same name" (they were "My Personal Exec Team" and "Exec-team"; similar, not identical). (6) Per Mac, xAI then "implemented and shipped a solution" requiring explicit user permission before an agent moves information to other channels. An xAI changelog entry dated 2026-10-11 (v0.70.2) adds: "After a bank or brokerage connector returns data, the Bot asks before sharing it anywhere else." That entry does not mention this incident.adversary_present: no (no attacker; a destination-resolution failure in ordinary use)severity: loss (private financial data shown to the operator's colleagues; a realised, non-monetary loss rather than a near-miss, because the exposure is the event; it rests on Mac's account and screenshot)direct_loss_usd: unknown (a privacy disclosure to colleagues; no monetary loss reported and none inherent)indirect_loss_usd: unknowndowntime: nonedata_exposure: Mac's personal account balances, his largest monthly expenses and personal finance notes, visible to members of XMTP Labs' private exec-team Slack channel for about two hours until a colleague flagged it (8:40 AM post to 10:36 AM flag, per the timestamps in his screenshot); deletion followed per Mac, and the exact deletion time and so the full exposure duration are unknown. ExplainX's about-two-hours dwell figure is its own estimate, not a measurement. Not reproduced heredetected_by: third-party (a colleague who saw the post in the exec-team channel flagged it to Mac by Slack DM)time_to_detect: about 2 hours (8:40 AM post, 10:36 AM DM, per the screenshot)time_to_recover: unknown exact interval; per his account he deleted the message after the colleague's flag, and Business Insider says he had already deleted it by the time the bot offered deletion. The screenshot timestamps establish the time to detection, not the deletion time. He then disconnected all his personal connectionsremediation: Mac deleted the post and disconnected Google, his calendars, his banking, Stripe "and everything" from his agentsstructural_fix: per Mac, an xAI permission step before agents move information to other channels; xAI's changelog v0.70.2 (dated 2026-10-11) records that after a bank or brokerage connector returns data, the Bot asks before sharing it anywhere else. Cited as consistent with Mac's account, not as xAI acknowledging this incidentcontrols_that_worked: the read-only scope on the bank accounts kept the event to a data disclosure rather than a funds action; a colleague's quick flag bounded the exposure window. Nothing prevented the disclosuretelemetry_grade: operator-logs (the operator's own screenshot of a Slack DM quoting the posted message, with its channel and timestamps; editable, single custodian, redacted by him; graded the same way as the victim's screenshots in PIR-2026-0038. No authenticated Slack export or audit log)sources:independence: weak. Every fact about the event (the post, its destination, the cause, the claimed xAI investigation and fix) comes from Mac, the operator, who has a commercial interest in agent-permission tooling. Futurism, Gadget Review and ExplainX are independent of him but relay his account and each say they could not verify it. The changelog is independent of Mac and is the vendor's own publication, but it describes a product change, not this incident, and its timing (dated Oct 11, published to the page between Oct 13 00:09Z and Oct 14 16:50Z) is looser than Mac's "shipped a solution last night" in an essay published Oct 9. The one Community Note is independent but cites no evidence beyond Mac's commercial interestconfidence: low to medium (the event is described consistently across Mac's post, screenshot and essay, and a matching vendor-side change followed; weakest links: a single interested party, no authenticated Slack record, no xAI statement)telemetry_grade set to operator-logs, not none as in the 0110 draft. Mac's screenshot shows a Slack DM quoting the posted message with its channel and timestamps; it is the operator's own, editable and redacted, which is exactly how PIR-2026-0038 grades the victim's Reddit screenshots. Grading it none here would be inconsistent with 0038.failure_locus moved from unknown to harness, still resting on Mac's account of the vendor's investigation, now with a matching vendor-side change. detected_by is third-party (a colleague, not the operator). The colleague's DM wording in the screenshot is shorter than Business Insider's rendering; the substance matches. No account numbers, balances or colleague identities from the screenshot are reproduced.